Как остановить и отключить Firewalld в CentOS 7
FirewallD — это комплексное решение брандмауэра, которое динамически управляет уровнем доверия сетевых подключений и интерфейсов. Это дает вам полный контроль над тем, какой трафик разрешен или запрещен в системе и из нее.
Начиная с CentOS 7, FirewallD заменяет iptables в качестве инструмента управления брандмауэром по умолчанию.
Настоятельно рекомендуется оставить службу FirewallD включенной, но в некоторых случаях, например при тестировании, может потребоваться ее остановка или полное отключение.
В этом руководстве мы покажем вам, как отключить FirewallD в системах CentOS 7.
Прежде чем приступить, убедитесь, что вы вошли в систему как пользователь с привилегиями sudo.
Проверьте состояние брандмауэра
Чтобы просмотреть текущий статус FirewallD, вы можете использовать команду firewall-cmd:
sudo firewall-cmd —state
Если служба FirewallD запущена, система выдаст следующее сообщение:
Отключить брандмауэр
Вы можете временно остановить службу FirewallD с помощью следующей команды:
sudo systemctl остановить firewalld
Однако это изменение будет действовать только для текущего сеанса выполнения.
Чтобы навсегда отключить брандмауэр в вашей системе CentOS 7, выполните следующие действия:
01. Сначала остановите службу FirewallD с помощью:
sudo systemctl stop firewalld
02. Отключите службу FirewallD для автоматического запуска при загрузке системы:
sudo systemctl disable firewalld
Вывод команды выше будет выглядеть примерно так:
Removed symlink /etc/systemd/system/multi-user.target.wants/firewalld.service.
Removed symlink /etc/systemd/system/dbus-org.fedoraproject.FirewallD1.service.
03. Создайте маску для FirewallD, которая предотвратит запуск брандмауэра другими службами:
sudo systemctl mask —now firewalld
Команда mask просто создает символическую ссылку из службы firewalld на /dev/null:
Created symlink from /etc/systemd/system/firewalld.service to /dev/null
Таким образом мы остановили и отключили брандмауэр на компьютере с CentOS 7.
Disable IPtables Centos 7 – How to Turn Off your Firewall
IPtables is a firewall tool in Linux that allows you to configure the IP packet filter rules of the Linux kernel firewall.
It is a rule-based firewall and comes pre-installed in most Linux operating systems. It works by monitoring incoming and outgoing traffic to and from your server using tables.
Tables contain a set of rules called a chain used to filter the data packets.
On the latest version of CentOS and RHEL operating systems like CentOS/RHEL 7, IPtables tool has been replaced by firewalld tool that provides a dynamically managed firewall.
However, if you are using IPtables for managing the firewall then you may need to disable it from your system in some cases.
In this tutorial, we will explain how to disable IPtables in CentOS 7.
Requirements
- A system running CentOS 7.
- A root password is configured.
Verify IPtables
Before starting, you will need to check whether IPtables is installed and running in your system or not.
First, check whether IPtables is installed or not with the following command:
rpm -qa iptables-services
If IPtables is installed, you should get the following output:
iptables-services-1.4.21-34.el7.x86_64
Next, verify whether the IPtables is running or not with the following command:
systemctl status iptables
If IPtables is running, you should get the following output:
● iptables.service — IPv4 firewall with iptables
Loaded: loaded (/usr/lib/systemd/system/iptables.service; disabled; vendor preset: disabled)
Active: active (exited) since Mon 2020-10-19 01:26:19 EDT; 4s ago
Process: 1198 ExecStart=/usr/libexec/iptables/iptables.init start (code=exited, status=0/SUCCESS)
Main PID: 1198 (code=exited, status=0/SUCCESS)
Oct 19 01:26:19 centos systemd[1]: Starting IPv4 firewall with iptables.
Oct 19 01:26:19 centos iptables.init[1198]: iptables: Applying firewall rules: [ OK ]
Oct 19 01:26:19 centos systemd[1]: Started IPv4 firewall with iptables.

You can now list all IPtables rules with the following command:
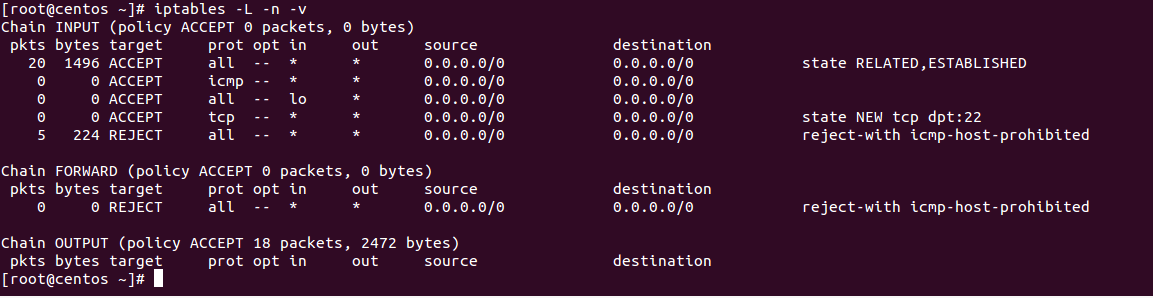
You should get the following output:
Chain INPUT (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
20 1496 ACCEPT all — * * 0.0.0.0/0 0.0.0.0/0 state RELATED,ESTABLISHED
0 0 ACCEPT icmp — * * 0.0.0.0/0 0.0.0.0/0
0 0 ACCEPT all — lo * 0.0.0.0/0 0.0.0.0/0
0 0 ACCEPT tcp — * * 0.0.0.0/0 0.0.0.0/0 state NEW tcp dpt:22
5 224 REJECT all — * * 0.0.0.0/0 0.0.0.0/0 reject-with icmp-host-prohibited
Chain FORWARD (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
0 0 REJECT all — * * 0.0.0.0/0 0.0.0.0/0 reject-with icmp-host-prohibited
Chain OUTPUT (policy ACCEPT 18 packets, 2472 bytes)
pkts bytes target prot opt in out source destination
At this point, IPtables is installed and running in your system. You can now proceed to stop and disable the IPtables.
Disable IPtables
First, it is recommended to flush all IPtables rules. You can do it with the following command:
Next, verify IPtables rules with the following command:
In the following output, you should see that all IPtables rules have been removed:
Chain INPUT (policy ACCEPT 9 packets, 596 bytes)
pkts bytes target prot opt in out source destination
Chain FORWARD (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
Chain OUTPUT (policy ACCEPT 5 packets, 488 bytes)
pkts bytes target prot opt in out source destination

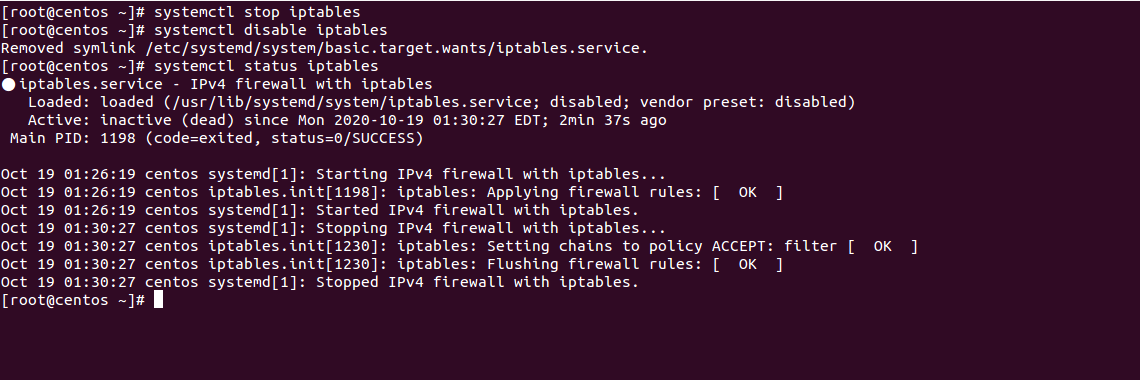
Next, stop the IPtables service by running the following command:
systemctl stop iptables
Next, disable the IPtables service to start at system reboot by running the following command:
systemctl disable iptables
You should get the following output:
Removed symlink /etc/systemd/system/basic.target.wants/iptables.service.
Conclusion
In the above guide, we’ve learned how to disable the IPtables on CentOS 7. We hope you now have enough knowledge to know how to disable the IPtables on CentOS 7. You can also enable the IPtables service again as per your requirements.
Recent Posts
- Forcepoint Next-Gen Firewall Review & Alternatives
- The Best JMX Monitoring Tools
- Best PostgreSQL Backup Tools
- Best CSPM Tools
- Best Cloud Workload Security Platforms
- Best Automated Browser Testing Tools
- Event Log Forwarding Guide
- The Best LogMeIn Alternatives
- Citrix ShareFile Alternatives
- SQL Server Security Basics
- Cloud Security Posture Management Guide
- Cloud Workload Security Guide
- The Best JBoss Monitoring Tools
- ITL Guide And Tools
- 10 Best Enterprise Password Management Solutions
Как запустить / остановить и включить / отключить FirewallD и Iptables Firewall в Linux
Как запустить / остановить и включить / отключить службу FirewallD
If you’re using CentOS/RHEL 7 or Fedora 18+ versions, you should follow below instructions to manage FirewallD service.
Start FirewallD Service
# systemctl start firewalld
Stop FirewallD Service
# systemctl stop firewalld
Check the Status of FirewallD
# systemctl status firewalld
Check the State of FirewallD
# firewall-cmd --state
As an alternative, you can disable the firewalld service so that it doesn’t apply rules to packets and enable ones needed again.
Disable FirewallD Service
# systemctl disable firewalld
Enable FirewallD Service
# systemctl enable firewalld
Mask FirewallD Service
# systemctl mask firewalld
Кроме того, вы можете замаскировать службу брандмауэра, которая создает символическую ссылку firewall.service на /dev/ null, тем самым отключая службу.
Unmask FirewallD Service
# systemctl unmask firewalld
This is reverse of masking the service. This removes the symlink of the service created during masking, thus re-enabling the service.
Как запустить / остановить и включить / отключить службу IPtables
On RHEL / CentOS 6/5/4 and Fedora 12-18 iptables firewall comes as pre and later, the iptables service can be installed via:
# yum install iptables-services
Then, the service can be started, stopped or restarted via following commands:
Start Iptables Service
# systemctl start iptables OR # service iptables start
Stop Iptables Service
# systemctl stop iptables OR # service iptables stop
Disable Iptables Service
# systemctl disable iptables Or # service iptables save # service iptables stop
Enable Iptables Service
# systemctl enable iptables Or # service iptables start
Check Status of Iptables Service
# systemctl status iptables OR # service iptables status
On Ubuntu and some other Linux distributions however, ufw is the command which is used to manage the iptables firewall service. Ufw provides an easy interface for the user to handle the iptables firewall service.
Enable Ufw Iptables Firewall
$ sudo ufw enable
Disable Ufw Iptables Firewall
$ sudo ufw disable
Check Status of Ufw Iptables Firewall
# sudo ufw status
However, if you want to list chains in iptables which contains all the rules following command can help you achieve the same:
# iptables -L -n -v
Как отключить iptables centos 7
А можно примеры этих самых GUI?
Ну если вы постоянно перемещаетесь вам проще иметь reject зону на вашем интерфейсе, интересный подход, особо если учесть что скорее всего ноут цепляется по вафле, а если RJ45, то вашему порту придет капец и довольно быстро. А че есть планшеты на федоре/ЦентОС/Рхел/ОралкЛинукс/СайтификЛинукс — просвятите?
Вы тока тока положили каменный топор(перешли на firewalld) и опять за старое(iptables привычней)?
с firewalld можно свой fial2bun написать, примитивный конечно, с этим я согласен. Ручками много правил придумывать, опять таки файл2бан для нубов которые не паряца, виндоусюзеры его любят ставить на свои впс с мегасупер сайтами на джумле и то не все.
не хватало кусок питона держать для генерации правил айпитаблеса.
> Ручками много правил придумывать, опять таки файл2бан для нубов которые не паряца,
Чот у меня прям день открытий на OpenNet.