Far cry 3. Что за вирус VirTool: Win32/Obfuscator.xz?
В конце установки Micrisoft security Essentials нашел какуето херь но не указал название вируса .
нужен ли этот файл Far cry ?
Описание: Эта программа используется для создания вирусов и других вредоносных программ.
Рекомендуемое действие: Немедленно удалите это программное обеспечение.


ска.
Нина Серебренникова
это кряк определился скорее всего за вирус. такая же история в resident evil 6 была. отправляет файл в карантин. отключаешь антивирус. с карантина берешь возобновляешь или ставишь на него разрешение. бывает, что может потребоваться перезагрузка. а без него игра не запустится.
Елена Селиверова
Игра пиратская? Возможно, антивирус определил «кряк» как вирус.
Это кряк, обеспечивает запутывание кода для запуска игр скачанных со стим. Обычно вреда не несут.
VirTool: Win32/Obfuscator — что это за вирус, как удалить?

Приветствую друзья! Работа компьютера зависит от софта, установленного на нем. Однако софт, как и железо — стоит денег, начиная с Windows и заканчивая небольшими утилитами. Часто, в погоней за халявой, мы получаем не только халявный софт но и вирусы на свой ПК.
VirTool: Win32/Obfuscator — что за вирус?
Компонент, предназначенный для изменения (обфускации) кода программы. Обычно используется чтобы антивирус не смог найти вирус.
Простыми словами — штука для маскировки, чтобы вирус было сложнее обнаружить.
Современные антивирусы знакомы с данным способом маскировки.
По факту — не вирус, а только инструмент для предотвращения обнаружения вируса.
Самое частое использование — взлом лицензионного ПО, а также игр Steam.
На заметку — расшифровка:
- VirTool — вирусная утилита (или хакерская).
- Win32 — приложение, работающее под Windows.
- Obfuscator — обусфактор (тип приложения).
Угроза обнаруживается на современных ОС (Windows 7/8/10).
Под названием VirTool: Win32/Obfuscator также может быть кряк, генератор ключей либо другой инструмент взлома. Например при установке пиратской игры антивирус может обнаружить угрозу с таким названием. Частая причина появление угроз — скачивание пиратских игр с торрента.
Угроза может быть найдена даже штатным антивирусом Microsoft Security Essentials (MSE). Возможно автоматические удаление, что логично.
VirTool: Win32/Obfuscator — как удалить?
Юзеры в интернете пишут — вреда VirTool: Win32/Obfuscator нет. Однако нельзя дать 100% гарантии, что в компонент не будет вшит настоящий вирус, например троян, активация которого произойдет автоматически при запуске.
Стоит проверить автозагрузку — нет ли там подозрительных записей. Рекомендую использовать AnVir Task Manager — бесплатный инструмент. Показывает содержимое автозагрузки (в том числе из реестра), список запланированных задач.
Просканировать ПК специальными утилитами двух направлений:
- AdwCleaner, HitmanPro — против рекламных вирусов/шпионов.
- Dr.Web CureIt!, Kaspersky Removal Tool — против опасных вирусов (трояны, ботнеты).
Мой совет: при отсутствии качественного стоящего антивируса рекомендую установить бесплатную версию Касперского. Базовой защиты более чем достаточно, но при этом абсолютно бесплатная, работает быстро.
Microsoft Security Essentials обнаружил угрозу, где видим что антивирус может как занести в карантин, так и удалить:

Внизу, под списком угроз можно узнать более подробное описание. Новички могут нажать Remove all для удаления всех угроз. Но учтите, после — некоторые игры могут перестать запускаться из-за отсутствия лицензии.
Сканер по требованию Microsoft Safety Scanner также способен обнаружить VirTool: Win32/Obfuscator:

Можно вручную проверить файл на вирусы при помощи сервиса VirusTotal. Перейдите на сайт, далее нажмите Выбрать файл (Choose file), укажите подозрительный файл. Дождитесь окончания проверки. Файл будет проверен десятками антивирусных движков (Kaspersky, ESET, NOD и другие).
Заключение
- VirTool: Win32/Obfuscator — скорее не вирус, а инструмент, который используется в работе вирусов, троянов и других.
- Удалить желательно, однако после — могут перестать корректно работать игры. Ведь инструмент используется при взломе ПО.
- В крайнем случае можно занести в исключения антивируса, тем самым, полностью разрешив работу VirTool: Win32/Obfuscator на свой страх и риск.
Не опасно устанавливать игру с VirTool: Win32/Obfuscator.xz?
Не составляет ли опасности установка на компьютер крякнутой игры, если она содержит VirTool: Win32/Obfuscator.xz, какие могут быть последствия?
комментировать
в избранное бонус
Vilia nt [19.4K]
9 лет назад
VirTool: Win32/Obfuscator.xz по сути своей является пиратской программой, путающей код определенного файла, не вирусом в типичном понимании этого слова. Как правило, ставят его для взлома игр приобретенных через Steam. Если Вы скачали не лицензионную современную игру с торрента, в 90% случаев антивирус обнаружит в одном из файлов VirTool: Win32/Obfuscator.xz.
Само-собой, антивирусы будут ее определять как вирус, так как программа предназначена для взлома игры, чем нарушаются авторские права, ни один из уважающих себя разработчиков антивирусного обеспечения не может программу для взлома считать приемлемой.
Лично я не слышал о негативных последствиях установки данного взломщика, сам несколько раз устанавливал игры с VirTool: Win32/Obfuscator.xz, никаких негативных последствий для компьютера не заметил.
VirTool:Win32/Vbinder
In this article you will locate concerning the interpretation of VirTool:Win32/Vbinder and also its adverse impact on your computer. Such ransomware are a kind of malware that is specified by on the internet frauds to demand paying the ransom by a victim.
It is better to prevent, than repair and repent!
When we talk about the intrusion of unfamiliar programs into your computer’s work, the proverb “Forewarned is forearmed” describes the situation as accurately as possible. Gridinsoft Anti-Malware is exactly the tool that is always useful to have in your armory: fast, efficient, up-to-date. It is appropriate to use it as an emergency help at the slightest suspicion of infection.
Gridinsoft Anti-Malware 6-day trial available.
EULA | Privacy Policy | Gridinsoft
Subscribe to our Telegram channel to be the first to know about news and our exclusive materials on information security.
Most of the instances, VirTool:Win32/Vbinder virus will certainly advise its targets to initiate funds transfer for the objective of neutralizing the amendments that the Trojan infection has actually introduced to the target’s tool.
VirTool:Win32/Vbinder Summary
These alterations can be as adheres to:
- Unconventionial binary language: Russian;
- The binary likely contains encrypted or compressed data.In this case, encryption is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Network activity detected but not expressed in API logs.Microsoft built an API solution right into its Windows operating system it reveals network activity for all apps and programs that ran on the computer in the past 30-days. This malware hides network activity.
- Anomalous binary characteristics.This is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Ciphering the documents found on the sufferer’s disk drive — so the victim can no more make use of the information;
- Preventing routine accessibility to the sufferer’s workstation.This is the typical behavior of a virus called locker. It blocks access to the computer until the victim pays the ransom.
This Article Contains:
VirTool:Win32/Vbinder
The most normal networks through which VirTool:Win32/Vbinder Trojans are injected are:
- By methods of phishing emails;
- As a repercussion of user ending up on a resource that holds a destructive software program;
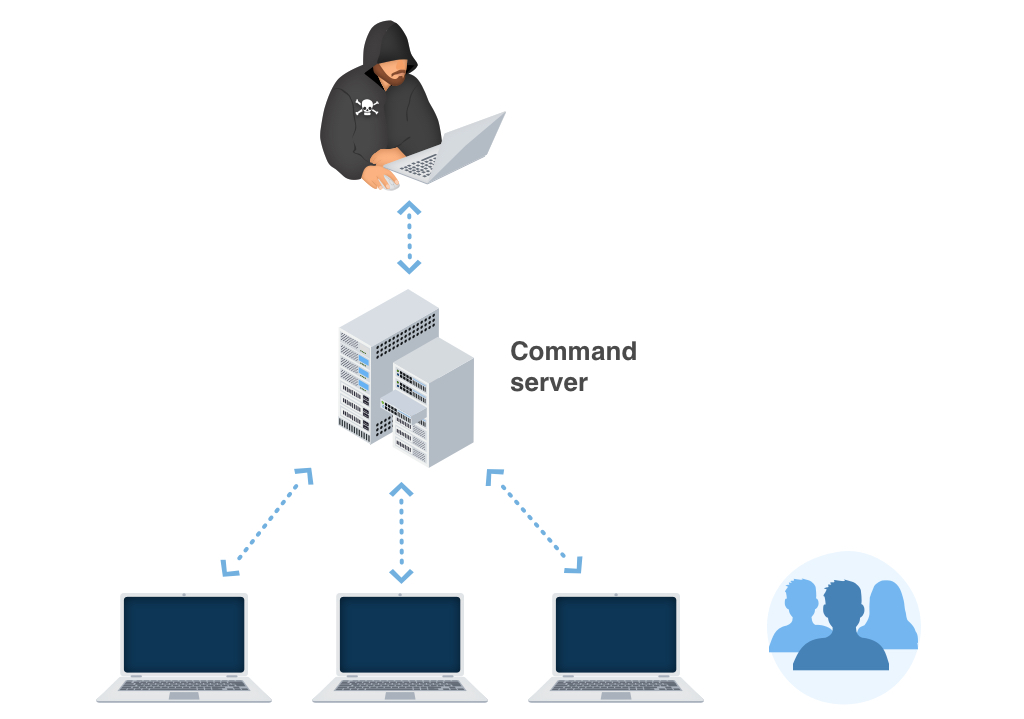
As quickly as the Trojan is efficiently injected, it will either cipher the information on the sufferer’s PC or avoid the device from functioning in an appropriate manner – while additionally putting a ransom money note that mentions the need for the sufferers to effect the repayment for the purpose of decrypting the papers or restoring the documents system back to the preliminary condition. In the majority of instances, the ransom note will come up when the client restarts the COMPUTER after the system has currently been damaged.
VirTool:Win32/Vbinder circulation networks.
In different corners of the world, VirTool:Win32/Vbinder expands by leaps as well as bounds. Nevertheless, the ransom money notes as well as tricks of obtaining the ransom amount may differ depending upon certain neighborhood (local) setups. The ransom notes as well as methods of extorting the ransom money quantity might vary depending on certain local (regional) settings.
Faulty alerts concerning unlicensed software program.
In certain areas, the Trojans commonly wrongfully report having actually found some unlicensed applications enabled on the victim’s gadget. The sharp then demands the user to pay the ransom.
Faulty statements about unlawful material.
In nations where software piracy is much less popular, this method is not as reliable for the cyber frauds. Additionally, the VirTool:Win32/Vbinder popup alert might incorrectly assert to be originating from a police establishment as well as will certainly report having located kid porn or various other unlawful information on the tool.
VirTool:Win32/Vbinder popup alert may incorrectly claim to be obtaining from a legislation enforcement organization and also will report having located kid pornography or other prohibited information on the tool. The alert will similarly include a requirement for the individual to pay the ransom.
Technical details
File Info:
crc32: 82947517md5: 0d46411728f5149a9e424596f1dff072name: by_cortxt.exesha1: 23797988d02189244ec8401e4251d9475c9990a0sha256: cb3a29816914c58f1b489a3493df1ccae03510f3c3a098bf4097010951db8179sha512: 90ab5e53104548ded7190801f671de229717a901eca0d74bfe6d6fccd1e0cb5c6791f4320da2d6692ca6747ee22e4ee5ae43fc46611853d1d2db72a49a53dc49ssdeep: 12288:jW05MBJtuLWsLypL8C0e4IO6Nz0gO0fLTA:d5MBJtu/uh8C/4IJjLTAtype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
CompanyName: ProductVersion: 0.0.0.1ProductName: x422x435x43ax441x442x43ex432FileVersion: 0.0.0.1FileDescription: x422x435x43ax441x442x43ex432x44bx439 x434Translation: 0x0419 0x04e4
VirTool:Win32/Vbinder also known as:
| GridinSoft | Trojan.Ransom.Gen |
| K7AntiVirus | Trojan ( 0040f2c01 ) |
| MicroWorld-eScan | Trojan.MSIL.Injector.MF |
| CMC | Backdoor.Win32.Poison!O |
| CAT-QuickHeal | TrojanDropper.Small.PQ4 |
| ALYac | Trojan.MSIL.Injector.MF |
| Malwarebytes | Backdoor.Dropper |
| BitDefender | Trojan.MSIL.Injector.MF |
| K7GW | Trojan ( 0040f2c01 ) |
| CrowdStrike | win/malicious_confidence_100% (D) |
| Arcabit | Trojan.MSIL.Injector.MF |
| Baidu | Win32.Trojan-Dropper.Small.o |
| Cyren | W32/GenTroj.S.gen!Eldorado |
| ESET-NOD32 | Win32/TrojanDropper.Small.NMM |
| TrendMicro-HouseCall | TROJ_VBINDER.SM |
| Paloalto | generic.ml |
| ClamAV | Win.Trojan.Poison-8692 |
| Kaspersky | Backdoor.Win32.Poison.ggrf |
| NANO-Antivirus | Trojan.Win32.Poison.cbeljp |
| ViRobot | Backdoor.Win32.Agent.67584.L |
| Rising | Dropper.Win32.Small.bnv (CLOUD) |
| Ad-Aware | Trojan.MSIL.Injector.MF |
| Emsisoft | Trojan.MSIL.Injector.MF (B) |
| Comodo | TrojWare.Win32.Ransom.Xorist.ET@4mg4hg |
| F-Secure | Heuristic.HEUR/AGEN.1022100 |
| DrWeb | Trojan.MulDrop8.22787 |
| Invincea | heuristic |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.fc |
| Trapmine | malicious.high.ml.score |
| Sophos | Troj/Vbinder-D |
| SentinelOne | DFI – Malicious PE |
| GData | Trojan.MSIL.Injector.MF |
| Jiangmin | Backdoor/Poison.abtg |
| Avira | HEUR/AGEN.1022100 |
| Microsoft | VirTool:Win32/Vbinder |
| Endgame | malicious (high confidence) |
| ZoneAlarm | Backdoor.Win32.Poison.ggrf |
| TACHYON | Backdoor/W32.Poison.402944.B |
| AhnLab-V3 | Backdoor/Win32.Poison.R72119 |
| Acronis | suspicious |
| McAfee | GenericRXAC-LG!0D46411728F5 |
| MAX | malware (ai score=100) |
| VBA32 | Backdoor.Poison |
| Panda | Trj/Injector.BH |
| Tencent | Win32.Trojan.Fakedoc.Auto |
| Yandex | Trojan.Oxij.Gen.LA |
| Ikarus | Backdoor.Poison |
| eGambit | Unsafe.AI_Score_99% |
| Fortinet | W32/Xorist.ET!tr |
| AVG | Win32:GenMalicious-NUS [Trj] |
| Cybereason | malicious.728f51 |
| Avast | Win32:GenMalicious-NUS [Trj] |
| Qihoo-360 | Win32/Backdoor.Poison.B |
How to remove VirTool:Win32/Vbinder virus?
Unwanted application has ofter come with other viruses and spyware. This threats can steal account credentials, or crypt your documents for ransom.
Reasons why I would recommend GridinSoft 1
The is an excellent way to deal with recognizing and removing threats – using Gridinsoft Anti-Malware. This program will scan your PC, find and neutralize all suspicious processes. 2 .
Download GridinSoft Anti-Malware.
You can download GridinSoft Anti-Malware by clicking the button below: